O.M.E.G.A
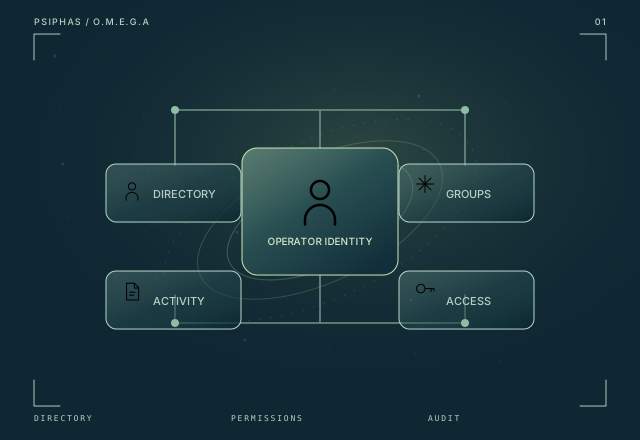
A unified Active Directory workspace for guided administration, operator-based permissions, and traceable enterprise identity operations.
Explore O.M.E.G.AAuthentication infrastructure
A shared authentication foundation for internal applications, connecting Active Directory identity with origin-bound profiles and application-specific access rules.
Project status
Built
Technology stack
Engineering focus
AD API Center brings repeated domain-authentication work into a central gateway. Application profiles keep access rules specific to each system, while a common interface connects internal applications, tools, and scripts to the same identity foundation.
01 / Context
Internal applications often need the same domain identity foundation while enforcing different access rules. Implementing that foundation separately in every application creates repeated work across tools, services, and scripts.
02 / The system
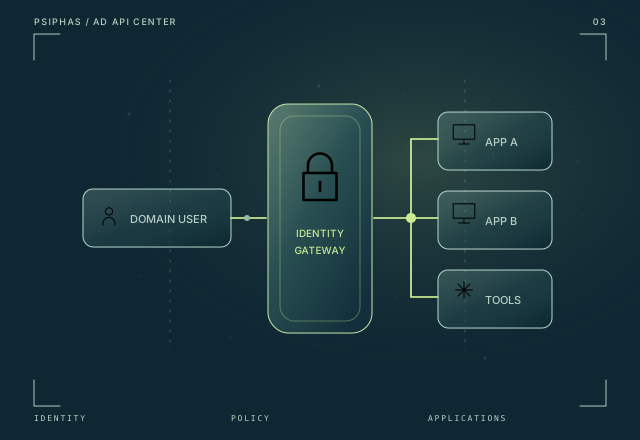
AD API Center separates common domain integration from application-specific access decisions. Each application receives a profile and an endpoint for checking the current domain user’s access. An administration interface manages rules, and origin binding ties each profile to the application that owns it. Active Directory lookups and authentication behavior sit behind the shared gateway.
03 / Capabilities
Profiles define access rules for individual applications, tools, and scripts.
Each application profile is tied to the origin that owns it, making that relationship part of the access model.
Active Directory lookups and authentication behavior are brought behind a shared gateway for internal HTTP and HTTPS systems.
04 / System map
This conceptual sequence explains how the project’s main capabilities connect.
An application profile captures the system’s access rules.
The internal application calls its assigned access endpoint.
The gateway handles the user’s domain identity and applicable rules.
The application receives the result for its own access workflow.
05 / Scope & status
Built for internal HTTP and HTTPS applications, tools, and scripts.
Continue exploring
A unified Active Directory workspace for guided administration, operator-based permissions, and traceable enterprise identity operations.
Explore O.M.E.G.A
A multi-agent security research engine that connects parallel investigations, target-specific testing, and benchmark evidence.
Explore RAVEN